WAPT AI
AI-powered web application penetration testing framework that combines traditional scanning with dynamic, LLM-generated payloads.
- Python
- Pentesting
- AI/LLM
Available for security work
B.Tech CSE student and hands-on security practitioner. I find and responsibly disclose vulnerabilities, build AI-powered offensive tooling, and spend my time breaking things so they can be fixed.
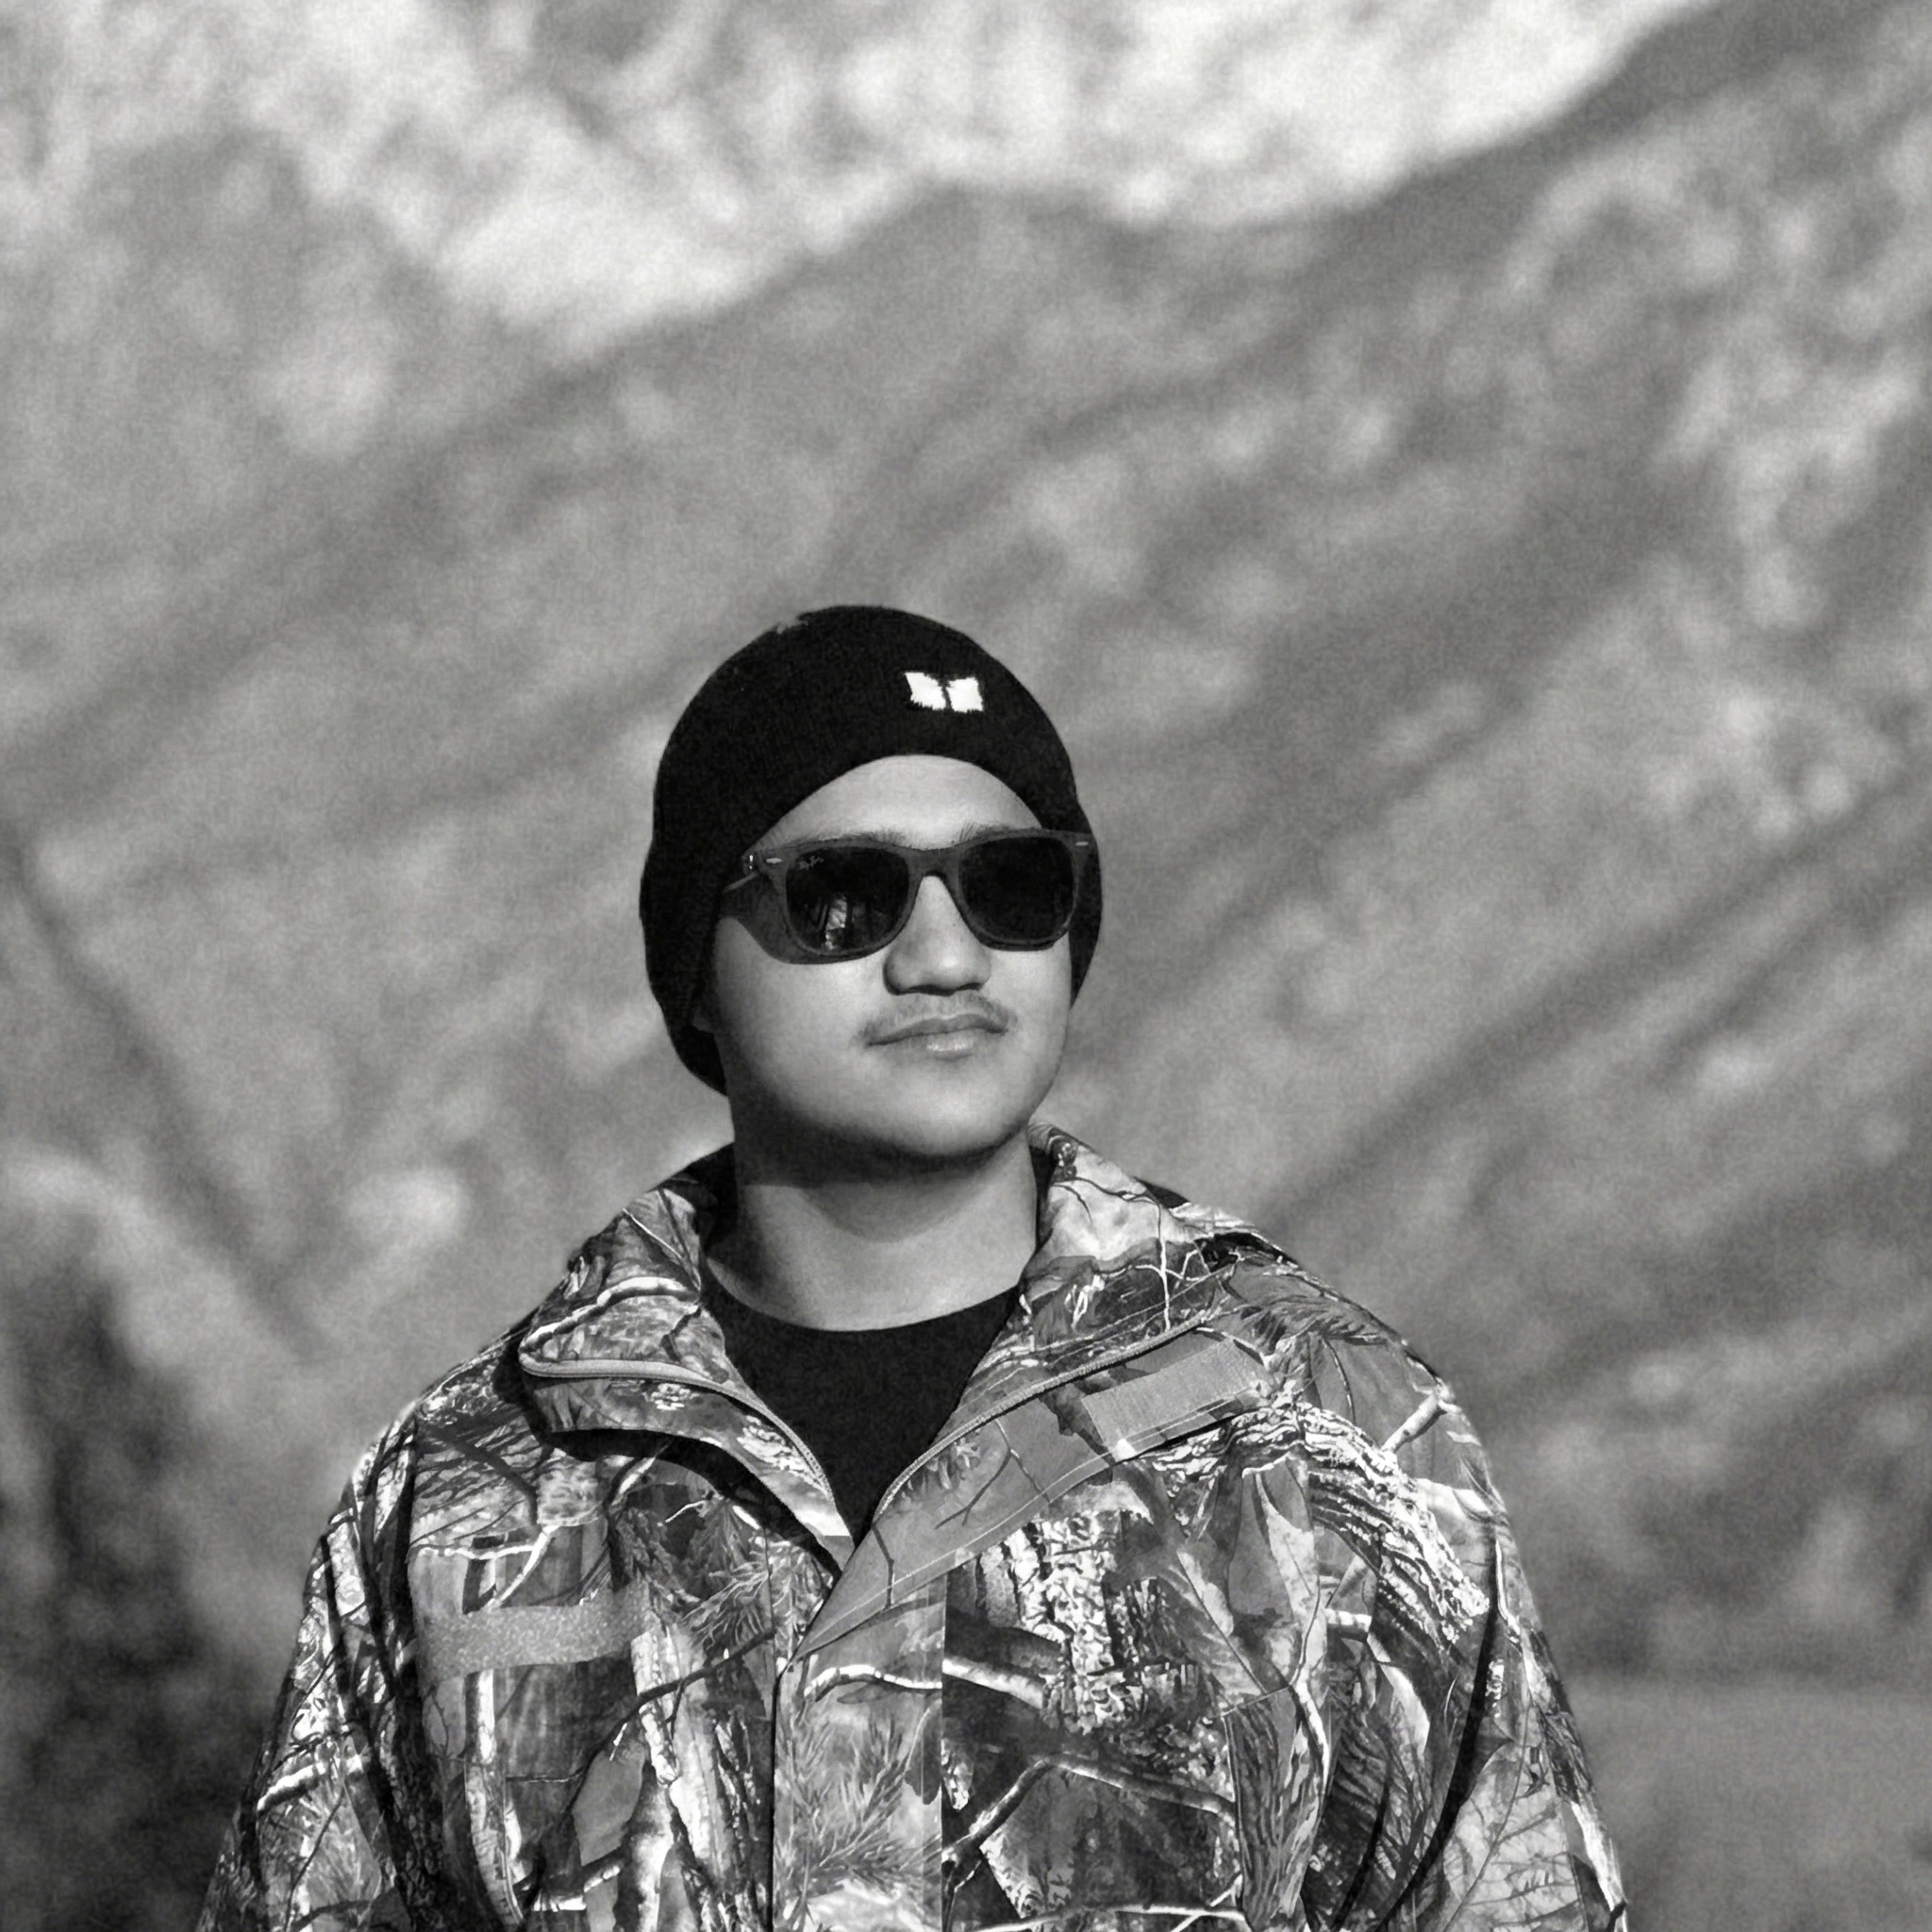
I'm a cybersecurity student at ABESIT, Ghaziabad, focused on offensive security — web application pentesting, network exploitation, and vulnerability research. My work sits where AI meets security tooling: automating reconnaissance, payload generation, and threat triage.
Outside of coursework I hunt bugs, publish CVEs, and build the tools I wish existed. I hold CRTA, CNSP, and Microsoft SC-200 certifications and I'm currently working on red team operations.
ENCODERSPRO Private Limited · Remote
ABESIT · Ghaziabad, Uttar Pradesh
AI-powered web application penetration testing framework that combines traditional scanning with dynamic, LLM-generated payloads.
Autonomous recon pipeline that chains enumeration → probing → crawling → vuln sweeps, with Claude-driven triage.
Responsibly disclosed vulnerabilities credited to me in the CVE program — all fixed by the vendor in the referenced releases.
Block name, alias and memo fields are joined into the (( reference autocomplete popup HTML without escaping in genHintItemHTML(). A crafted block self-fires on search, escalating to OS command execution via Electron.
The file-tree picker's hover tooltip builds an aria-label from document metadata without escaping in pathName.ts. A double quote breaks out of the attribute and injects an event handler, reaching child_process on hover.
confirmDialog() inserts package and notebook names into innerHTML without escaping. A malicious bazaar package whose name carries HTML executes when a user uninstalls a package or unlocks an encrypted notebook.
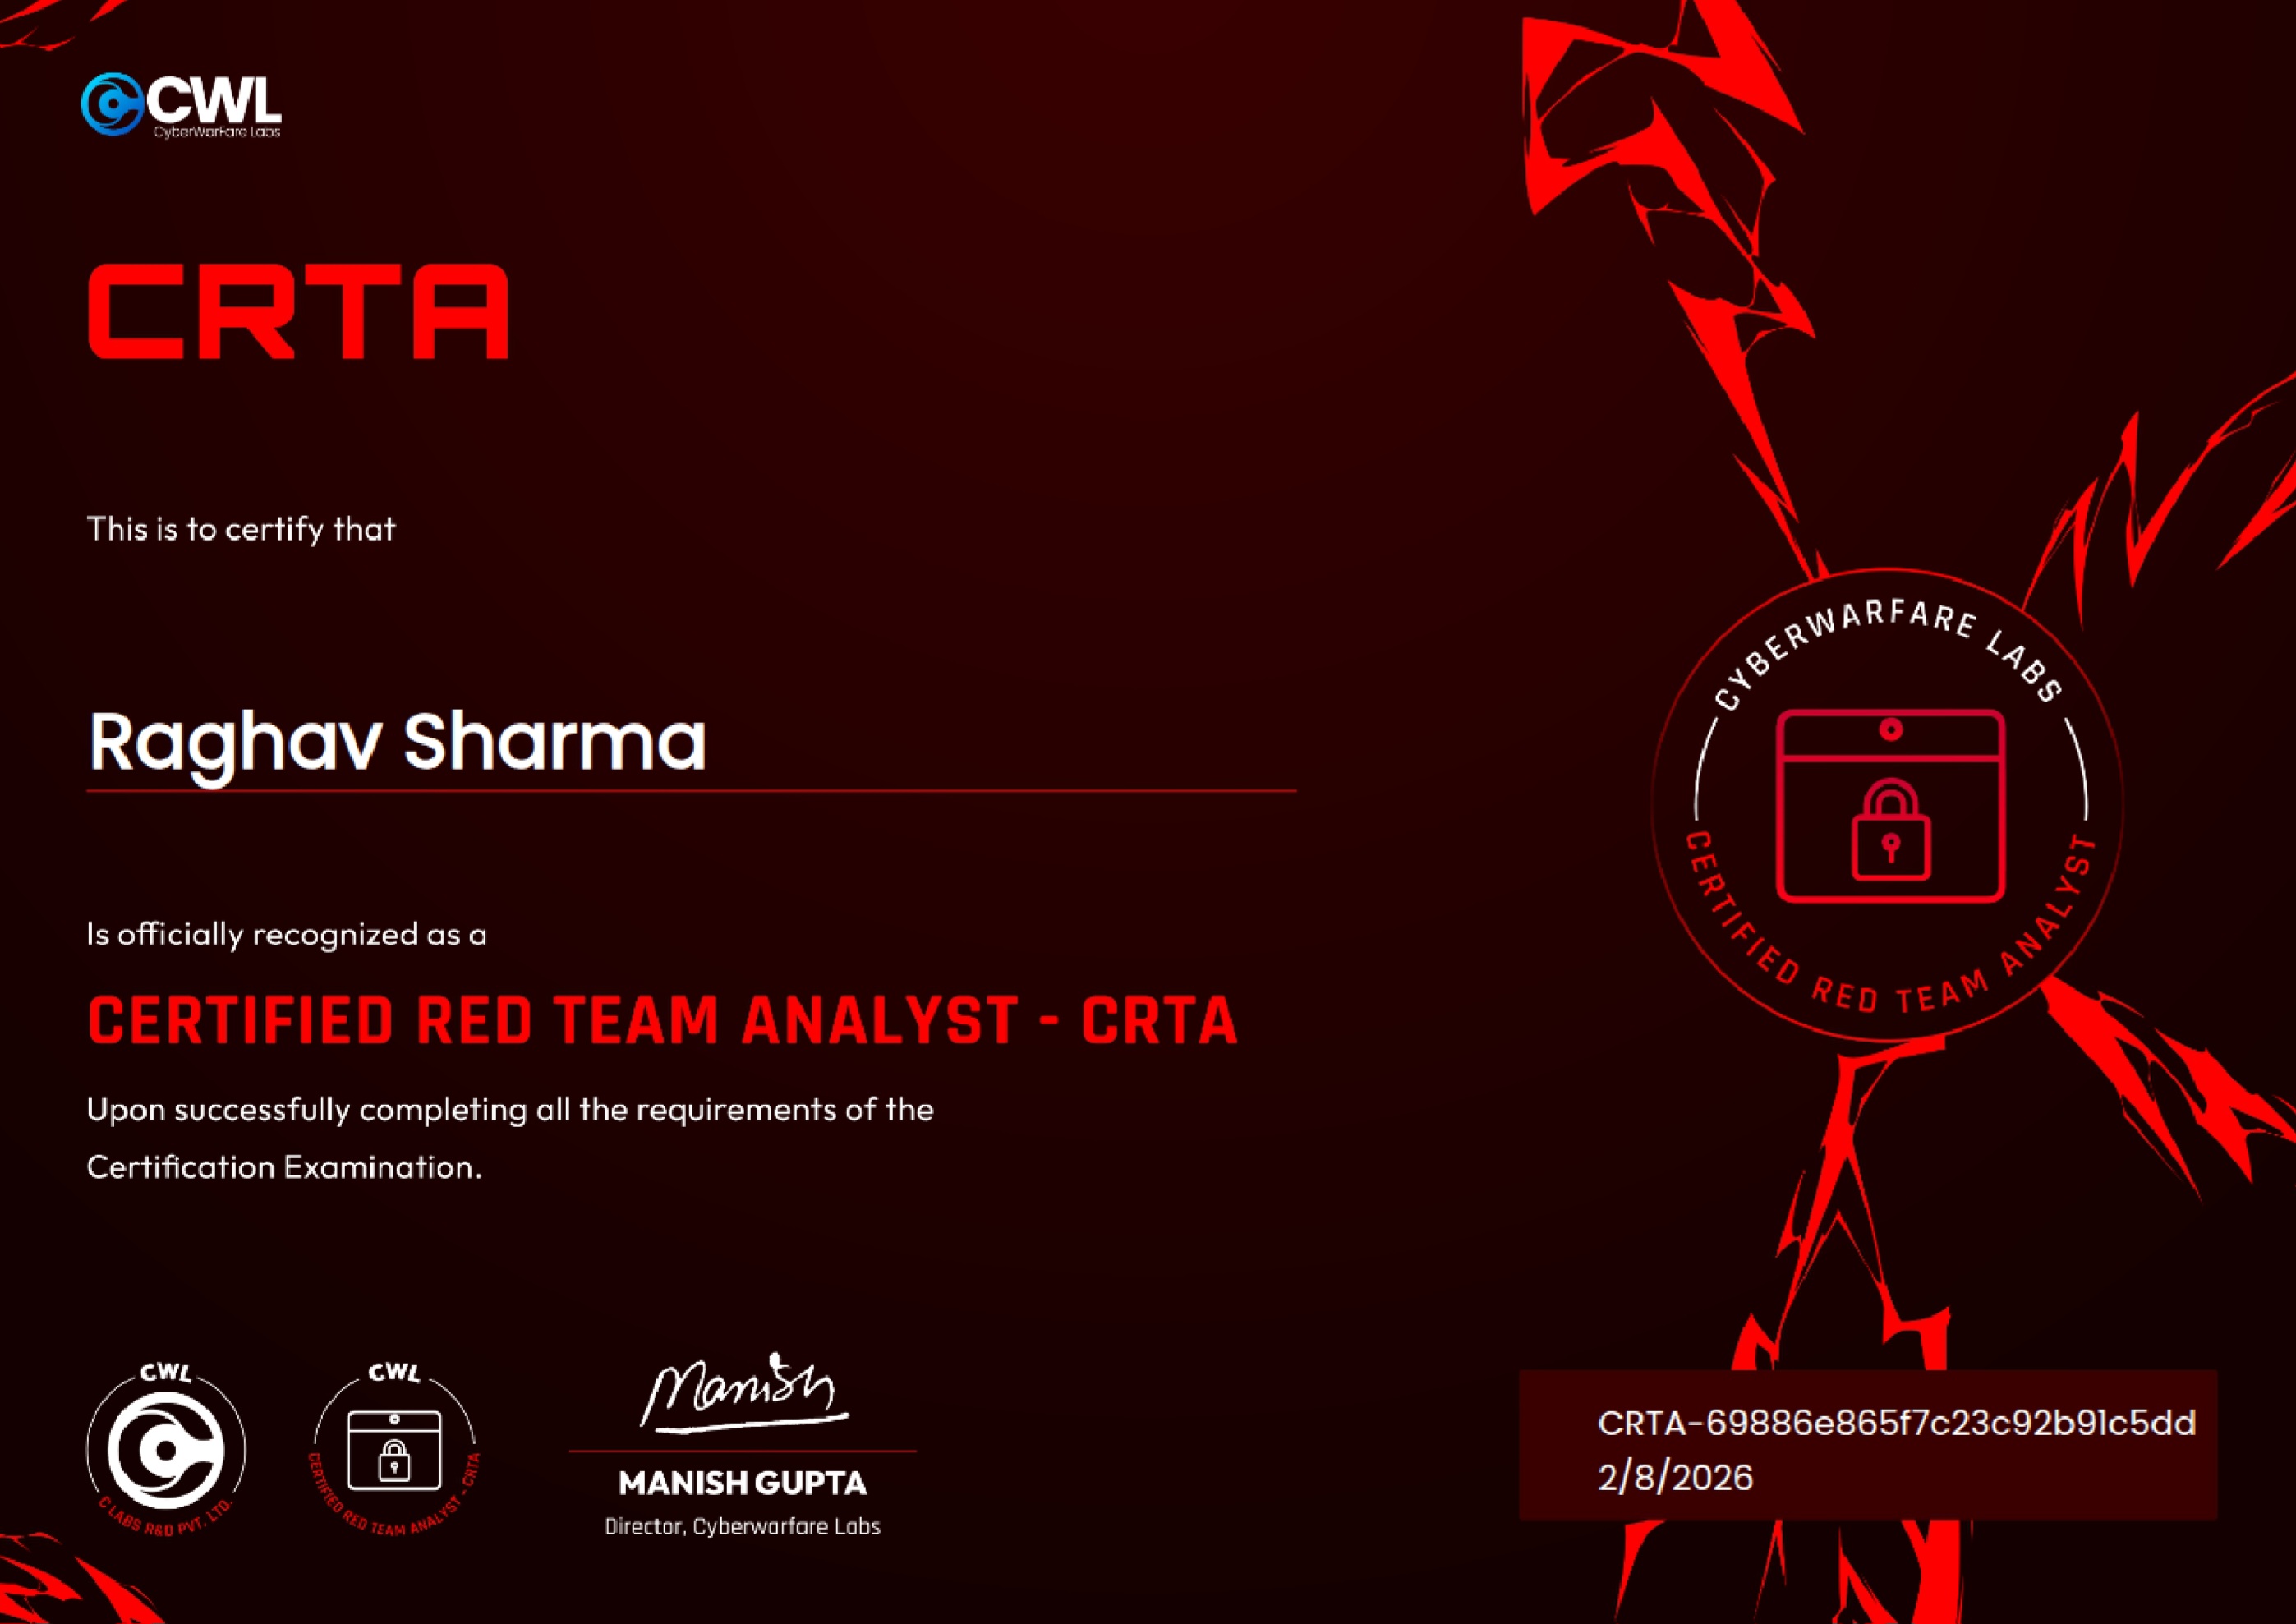
CyberWarfare Labs
Issued Feb 2026
Hands-on red teaming examination validating practical offensive security and adversary simulation skills.
Verified
Microsoft
Issued Aug 2026
Detecting, investigating and responding to threats with Microsoft Defender and Microsoft Sentinel.
Verified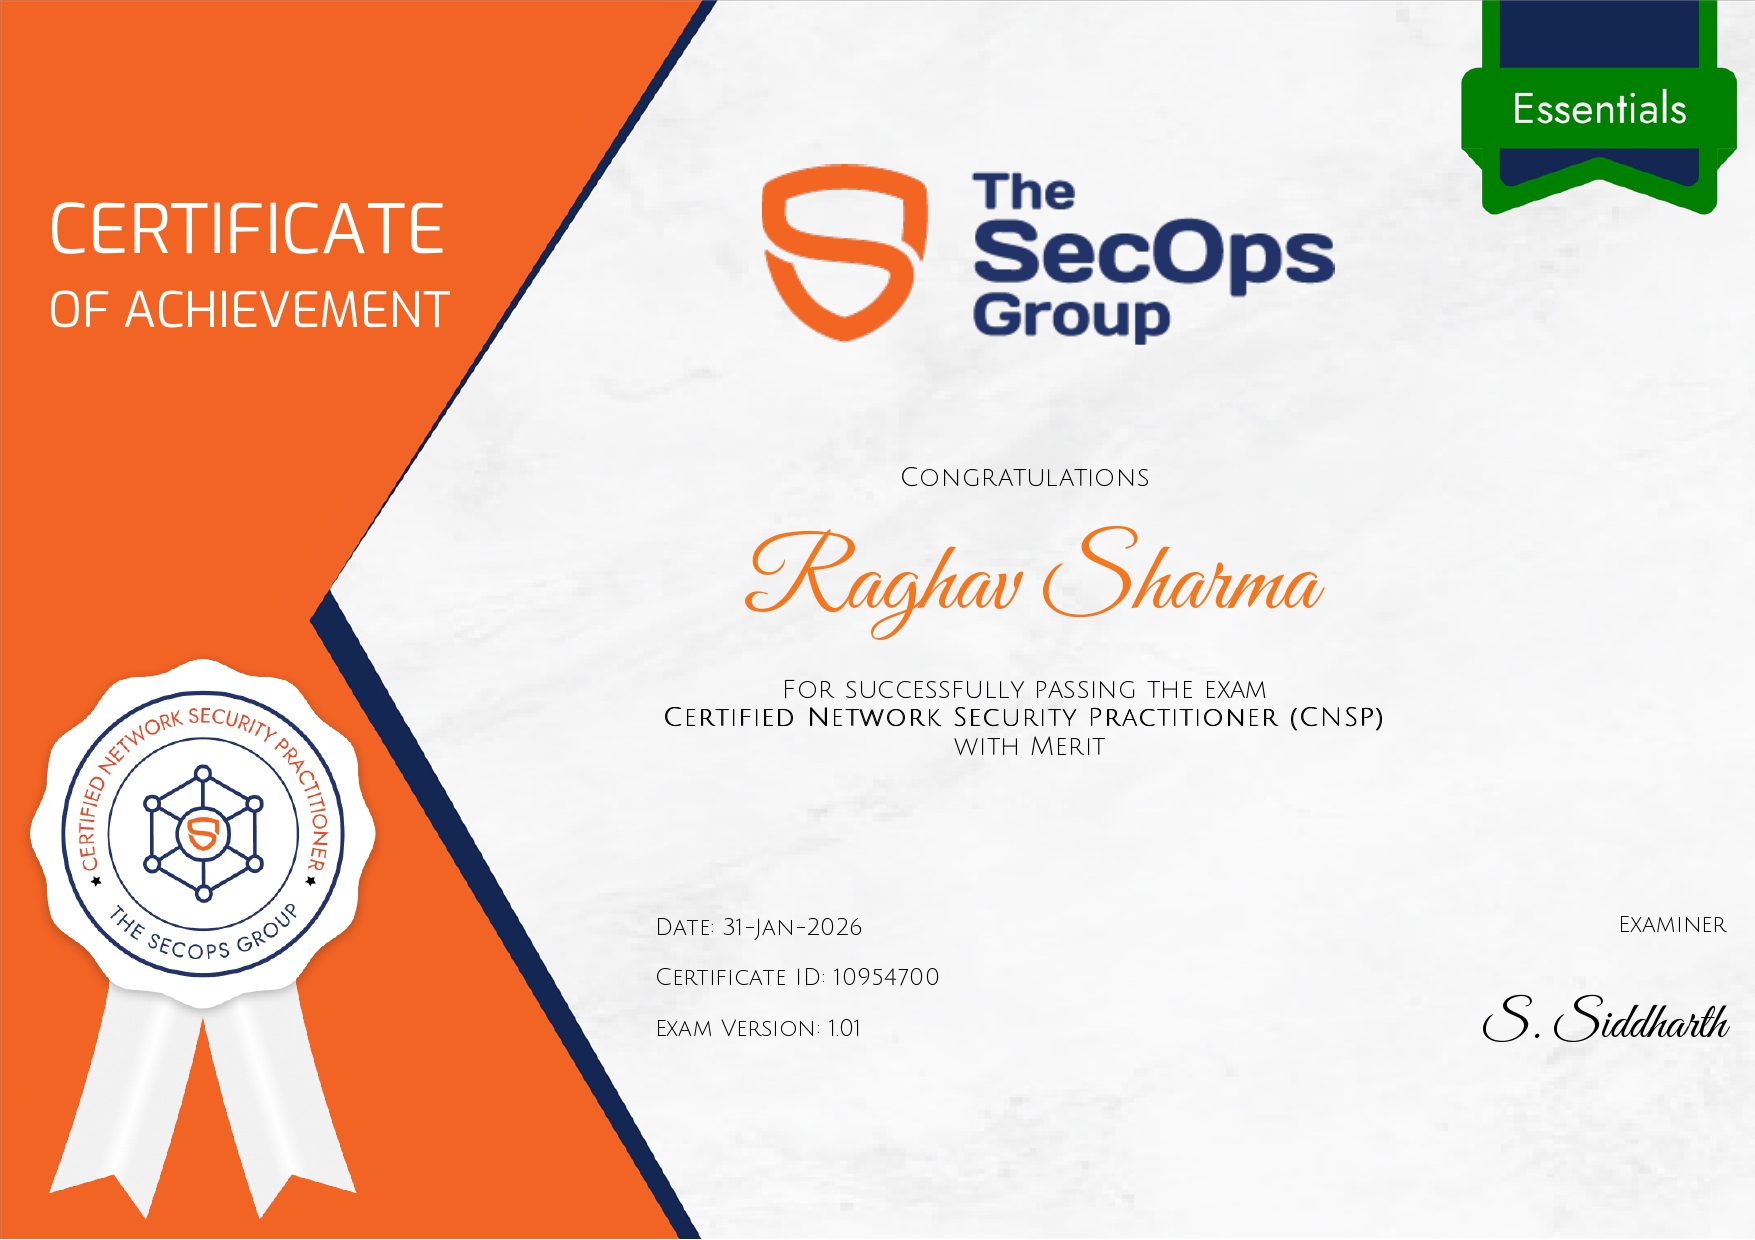
The SecOps Group
Issued Jan 2026
Practical network security exam covering threat detection, defence configuration and real-world security operations.
Verified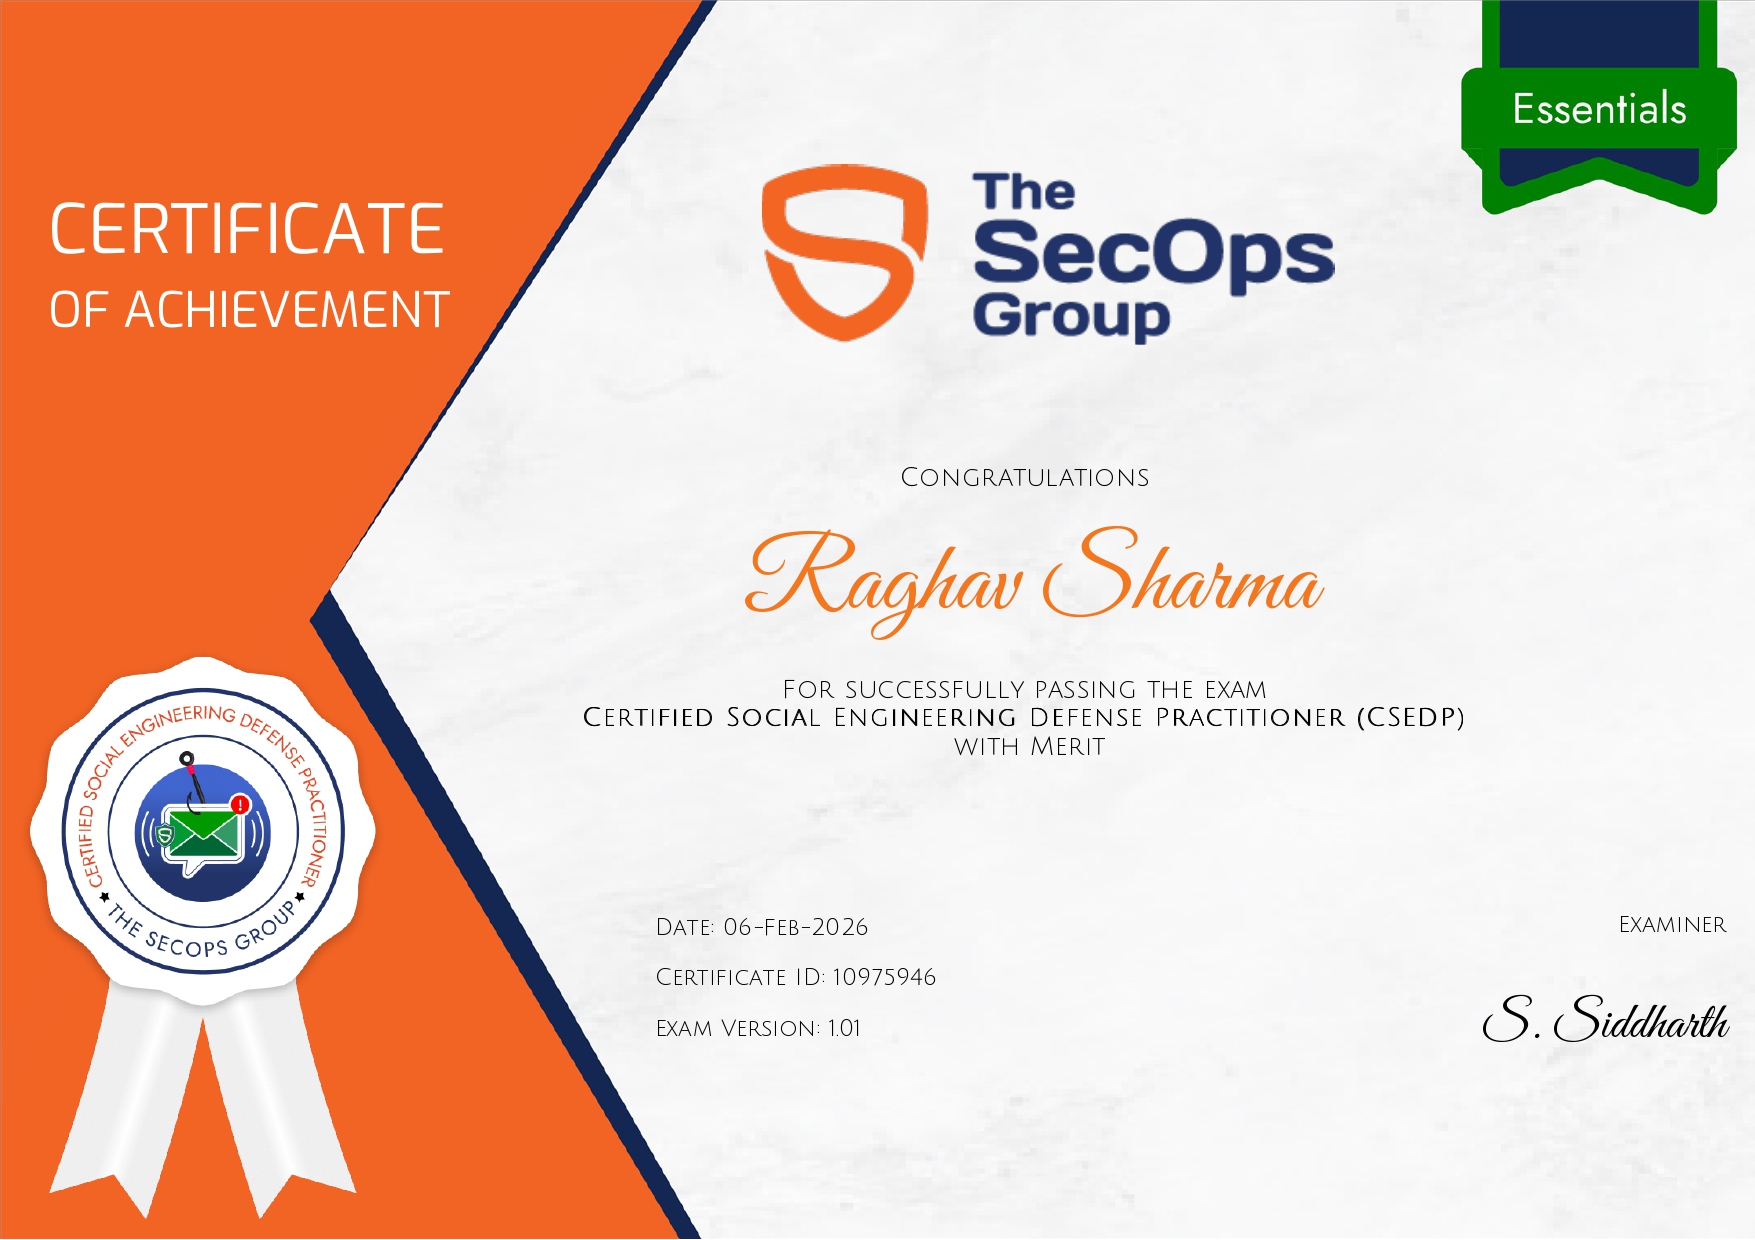
The SecOps Group
Issued Jan 2026
Detecting manipulation tactics and protecting organisations from deception-driven attacks.
VerifiedOpen to security internships, pentesting engagements, and collaboration on offensive tooling. The fastest way to reach me is email.
wrk.raghav@gmail.com